One line · ~30 words
Kenio Shirley is a fractional CTO for regulated platforms who has delivered a FedRAMP Moderate authorization and cut change-approval time by 30% at a HIPAA business associate.
Everything a journalist or podcast booker needs to cite Kenio Shirley accurately, without sending an email first.
Use whichever length fits. These are the approved wordings — please quote them verbatim rather than paraphrasing.
Kenio Shirley is a fractional CTO for regulated platforms who has delivered a FedRAMP Moderate authorization and cut change-approval time by 30% at a HIPAA business associate.
Kenio Shirley is a fractional Chief Technology Officer for regulated platforms and the founder of HireKen.io. He takes cloud companies through the audits that gate their revenue: he has taken a system through FedRAMP Moderate authorization, and over 15 years has led cloud and engineering teams through SOC 2, SOX IT general controls, HITRUST and PCI DSS examinations. His method is a change record that satisfies every framework at once — at a HIPAA business associate it cut change-approval time by 30% with no major incidents. He is based in New Jersey.
Kenio Shirley is a fractional Chief Technology Officer for regulated platforms and the founder of HireKen.io. He takes cloud companies in healthcare, financial services and government technology through the audits that gate their revenue. He has taken a system through FedRAMP Moderate authorization via an Agency ATO, and has led ISM readiness and remediation advisory for organisations selling into Australian government at the OFFICIAL classification level. Over more than 15 years he has led cloud and engineering organisations through SOC 2 CC8.1, SOX IT general controls, NIST 800-53 control families, HITRUST and PCI DSS examinations. His premise is that audit programs fail on the change record rather than the technology, and that a change advisory board is a design problem, not a compliance tax: at a HIPAA business associate he cut change-approval time by 30% while keeping the evidence trail intact and shipping no major incidents. He holds a Master of Science in Information Technology Management from Western Governors University and is based in New Jersey.
The web-resolution portrait is below and free to use with the credit line. A print-resolution file is available on request and sent the same day.
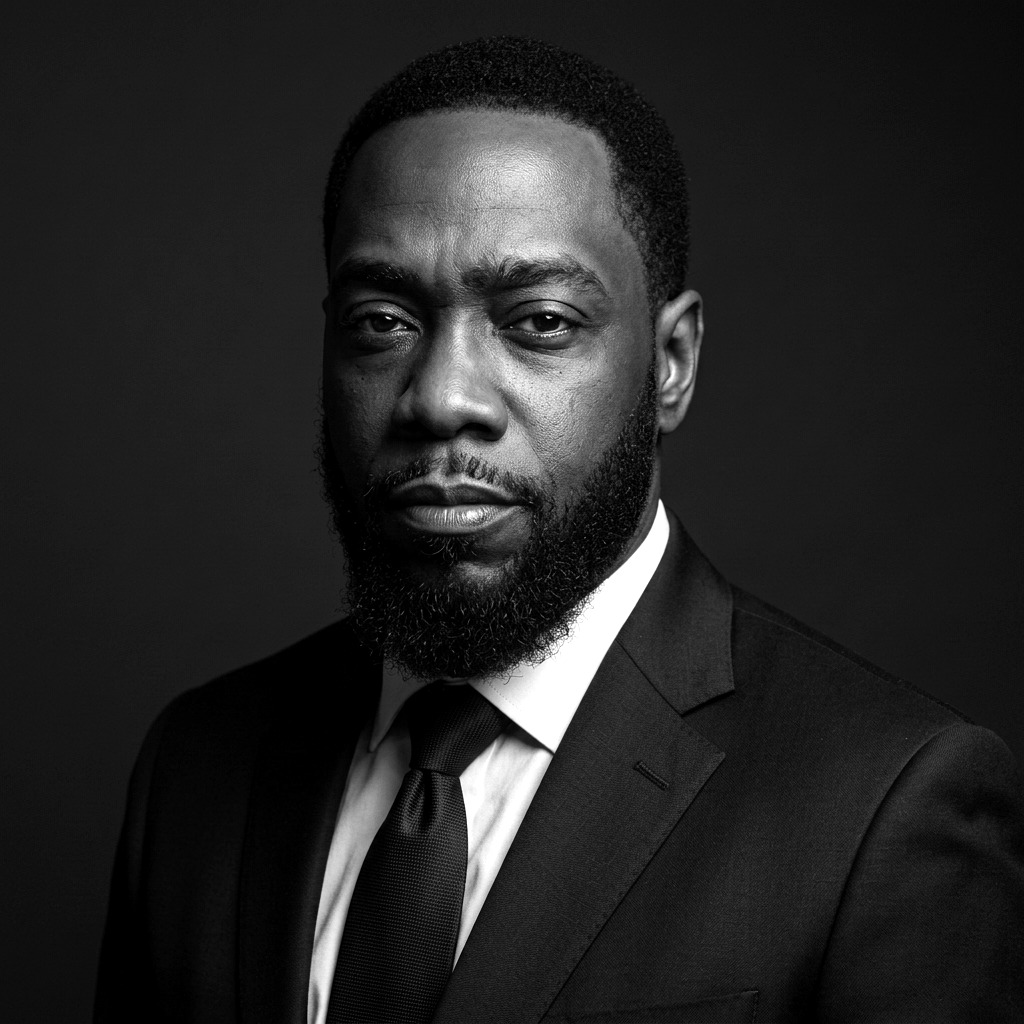
Credit line: Photo courtesy of Kenio Shirley
Five subjects Kenio can speak to in depth, with the angle he takes on each.
Authorization boundary decisions, continuous monitoring and the change-management discipline that keeps a system inside its authorization.
Why most SOX ITGC and SOC 2 CC8 findings trace back to population completeness, access reviews and change evidence — and how to fix them before the auditor arrives.
What changes when a bad deploy is a breach rather than an outage, and how that reshapes control design for ePHI platforms.
Two ownership changes, two control environments merging, and the specific places auditors find the gaps in the first 90 days.
Model versions, prompt changes and retraining as configuration items, and how SOC 2, ISO 27001 and emerging AI assurance schemes are starting to ask for them.
Starting points a host can use as written, or bend to their format.
Booking and press enquiries go to iam@kenioshirley.com. Background on his work is on the about page, and his practice is HireKen.io.